IMF Tokenized Stocks Study: 24/7 Demand, 80% Fractional Trades and Liquidity Risks

More than half of trading in the tokenized equities examined by the International Monetary Fund occurred outside regular U.S. equity-market hours. Approximately 80% of transactions were smaller than one conventional share. Those are substantial signals of what users want from a tokenized stock: a way to trade when U.S. exchanges are closed and a way to buy a fraction of an expensive share.  The same study finds that these markets are considerably less liquid and roughly 1.5 times as volatile as the equivalent traditional stocks. That matters for anyone assuming that round-the-clock access necessarily improves execution quality.  The results appear in Chapter 3 of the IMFs October 2026 Global Financial Stability Report, Scaling Tokenization: New Efficiencies, New Vulnerabilities, publicly discussed ahead of the full report release. Public discussion intensified in October 11 reporting. The IMFs empirical observations deserve close reading because they answer a different question from recent exchange launches: how do tokenized stocks actually trade after they exist?What the IMF measured  The IMF compared five liquid tokenized U.S. equity-linked instruments with corresponding conventional assets, using products from Ondo Finance and xStocks. The exercise covered 11 centralized and decentralized trading venues, 365 trading days, and more than two million five-minute observations of prices
20 hours agoIndustry Research

Papertrade Price-Feed Manipulation: $1.28M Wallet, ETH Midpoint and LP Risk

A wallet withdrew about $2.48 million from Papertrade after depositing approximately $1.2 million, according to transaction records reviewed by The Block on October 11. The roughly $1.28 million difference became the focus of an unusually concrete dispute over how a new 1,000x perpetuals venue prices its trades. The activity centered on ETH orders placed on Hyperliquid while the same wallet held much larger synthetic positions on Papertrade.  The earlier October 11 analysis of Papertrade examined an estimated $11 billion of open notional, roughly $54 million of trader margin in one snapshot, and the difference between open interest and funds available to honor winners. The new evidence is about how a trader may influence the price that determines those winners and losers. It calls for an update to that existing analysis, not a second general introduction to leverage.A price move of 0.12% can matter enormously at 1,000x  Papertrade settles synthetic trades against a pool rather than matching each customer with a second trader. Its reference price comes from the midpoint between Hyperliquids best bid and offer. A synthetic position can therefore be highly sensitive to changes at the top of a separate venues order book.  The Block reported that, between 6:01 and 6:02 p.m.

20 hours agoIndustry Research

Pando Finance to launch Hong Kong's second spot Solana ETF on October 13

Pando Finance Limited has announced plans to list its spot Solana exchange traded fund on the Hong Kong Stock Exchange on October 13, becoming the citys second investment product offering direct exposure to SOL.  SummaryPando‘s spot Solana ETF is expected to list in Hong Kong on October 13, becoming the city’s second fund offering direct exposure to SOL.Subscriptions run from October 6 to 12, with shares priced between HK$7.80 and HK$8 and a minimum trading lot of 100 shares.The fund will charge a 0.6% annual management fee, compared with 0.99% for ChinaAMCs existing Solana ETF.HashKey Exchange will handle SOL transactions, while HashKey Custody Services will safeguard the assets. The fund will not use staking, derivatives or leverage.  According to the funds subscription details, the Pando Solana ETF (02831) is accepting applications from October 6 through October 12, with an indicative issue price of HK7.80toHK8 per share.  Investors can subscribe in lots of 100 shares, bringing the minimum entry cost to approximately HK$800 before brokerage charges and other applicable fees.  Although the fund uses the US dollar as its base currency, its shares will trade in Hong Kong dollars on the local exchange.  Pando has set an annual management fee of 0.6%, while its estimated annual

20 hours agoIndustry

Bank of Korea won't issue stablecoins: Here's why

The Bank of Korea has ruled out directly operating stablecoin businesses, with Governor Hyun Song Shin telling lawmakers on October 12 that private companies should handle their issuance and operations while the central bank continues developing its institutional digital currency system.  During a parliamentary audit held at the Bank of Korea headquarters in Seoul, Shin said private businesses were the appropriate operators of stablecoins, while the central bank would continue providing input on monetary stability and payment systems. The governor made the remarks while responding to questions from independent lawmaker Lee Jun-seok about stablecoins, bank deposit tokens and central bank digital currencies (CBDCs). He distinguished privately operated stablecoins from Project Hangang, the central banks ongoing initiative involving institutional digital currency and commercial bank-issued deposit tokens.  Bank of Korea says private companies should handle stablecoins  At the October 12 parliamentary hearing, Shin explained that stablecoins should be operated by private companies because they are designed to circulate through decentralized blockchain networks. He described their purpose as allowing digital tokens to move independently of central bank currency on permissionless blockchain systems. However, the governor maintained that the Bank of Korea would retain a role in discussions concerning the countrys monetary system.  Shin stated that “it is

20 hours agoIndustry

THORChain dev accuses Tether of temporarily freezing USDT vaults

THORChain technical co-founder Chad Barraford accused stablecoin issuer Tether of blacklisting the networks USDt (USDT) vaults without explanation, then unfreezing them hours later.  In a Friday X post, Barraford said that Tether had blacklisted THORChain vault addresses, freezing about a combined 1.45 million USDT in the networks funds across four wallets. He reported about two hours later than trading would resume after the company unfroze all the addresses.  “We dont know why this choice was made and have had no comms with USDT before this action and are actively reaching out to have a conversation,” said Barraford before the addresses were unfrozen. “We hope that this was made in error / misunderstanding.”  Cointelegraph reached out to Tether and THORChain for details on the incident, but did not receive an immediate response.  Earlier this week, cross-border payments platform Conduit Technology filed a lawsuit against Tether, alleging that the stablecoin company froze $2.76 million worth of USDt in a wallet tied to an investigation launched by Brazilian authorities in 2024. Two Thai nationals also sued the stablecoin company in August for allegedly freezing $42.4 million in USDt after an alleged “informal request” from US Homeland Security Investigations.

20 hours agoIndustry

Ledger CryptoBilis Update: Confirmed Hardware Implant, Loss Estimates Still Unverified

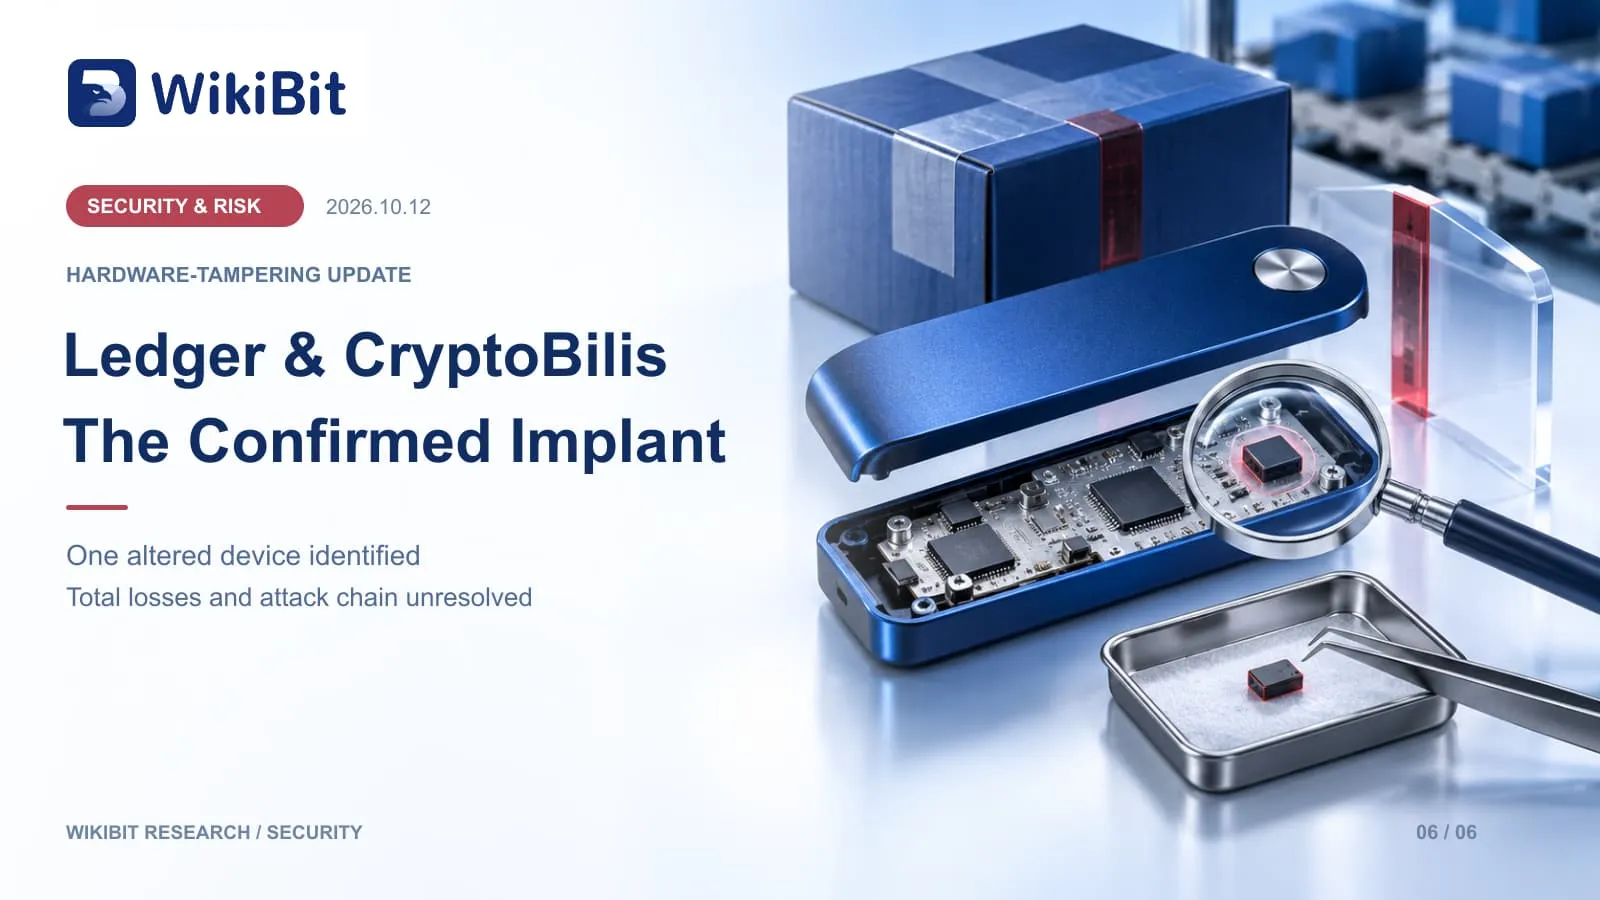
The Ledger–CryptoBilis investigation has moved beyond a hypothetical supply-chain compromise. On October 10, Ledger confirmed that an affected customers device contained an unauthorized hardware implant. That is substantially different from the companys initial October 9 request for the Southeast Asian reseller to stop selling and shipping wallets while it investigated reports of missing funds.  The physical finding matters because it establishes that at least one affected device was modified. It does not establish how many devices were altered, how the implant entered the distribution chain, whether it caused every reported theft, or how much money the perpetrators ultimately controlled. Those are distinct questions. The companys reported implant finding is stronger evidence than the original rumors; it is not an audited final incident report.What the company has confirmed  Reporting on Ledgers October 10 support-account update says the company identified an unauthorized implant inside one users device. CryptoBilis suspended sales of hardware wallets while the investigation continued. Ledger also said it had found no indication that its own security infrastructure, systems or services had been compromised. That last assertion is a statement of the companys current investigation, not independently established proof that every step of its manufacturing and distribution chain has been cleared.  The original

20 hours agoIndustry Research

Kraken October 2026 Delistings: 13 Assets, Trading and Withdrawal Deadlines

Krakens October 2026 delisting notice places 13 assets on a path toward forced liquidation in February 2027. Customers who leave their holdings on the venue after withdrawals close may receive far less than recent quoted prices, and Kraken expressly warns that some residual positions could produce minimal or no proceeds.  The exchanges English notice, last updated October 8, gives three dates: trading and deposits end October 23, 2026 at 14:00 UTC; withdrawals end January 29, 2027 at 15:00 UTC; and remaining balances are subject to automatic liquidation February 1–12, 2027. These are different operational events. A coin can still appear as a custodial balance after trading stops, but that does not mean a holder can later choose a market exit or expect a guaranteed conversion price.Which assets are in the official batch?  The current English notice names BMB, ELX, APU, BDXN, DUCK, BOS, U, OBOL, IDEX, FIS, UXLINK, ALTHEA and NOBODY. That is 13 assets. The current accessible Norwegian and Chinese language pages contain the same list.  The matching language versions provide useful corroboration of the current batch. They do not establish what a future asset-specific notice might say, and they cannot replace checking account-specific venue restrictions. The confirmed October list should not

20 hours agoIndustry Research

COLDCARD’s X Phishing Post: What Was Compromised and What Remains Unknown

Bitcoin hardware-wallet maker COLDCARD said an unauthorized phishing post appeared on its official X account on October 11, 2026. The post was removed. The company told users not to follow or interact with the malicious link and said it had contacted X while examining account access. The immediate verified exposure is an official-channel impersonation incident—not proof that the current event compromised device firmware, wallet keys or the vendors infrastructure.A trusted account carried an untrusted instruction  Hardware-wallet users often rely on vendor announcements to identify firmware updates, security emergencies and device setup guidance. An attacker who can place a post on a verified-looking official channel can turn that trust into a route to a phishing site. Even a person who owns a genuine, uncompromised hardware wallet may be harmed if they manually disclose the recovery phrase or sign an unrelated transaction after following such a message.  COLDCARD said it had used offline two-factor authentication and tightly restricted access for its X account since 2017. Its representatives said the account logs and authentication records did not show a corresponding suspicious session, and asked X to investigate. This does not establish that Xs internal administration tools were breached; platform-side access is a hypothesis that the

20 hours agoIndustry Research

XRPL Batch Wrapper Bug: A Consensus and Indexer Failure Prevented

XRPLs October 9 security report describes a second, independent flaw in the Batch transaction feature. Unlike the payment-engine overflow, this bug threatened ledger availability and data compatibility, not the supply of XRP. A crafted inner-transaction wrapper could have been interpreted differently by servers on different versions. The developers say Batch had not been activated on Mainnet when the bug was found, and no funds were lost and no consensus failure occurred.Why a field name could split a network  Batch allows a group of signed transactions to be submitted together. Each inner transaction is supposed to be carried inside a field called RawTransaction. The faulty validation logic accepted other object-type wrapper fields if that field had no restrictive template.  Older xrpld 3.3.0 and newer 3.4.0 defined different object fields. A deliberately nonstandard Batch payload could be accepted and relayed by one version but fail deserialization in another. If enough validators ran the incompatible combinations, the trusted validator group could disagree on the contents of a ledger and potentially stop validating new ledgers.  The technical issue is distinct from private-key theft. Every inner transaction still required ordinary valid signatures and balance checks. The attacker could not simply authorize another users payment without that users signature.

20 hours agoIndustry Research

XRPL Payment Overflow: How a Critical XRP Supply Bug Was Patched

The XRP Ledger avoided a potential supply-integrity failure that, in a deliberately constructed test, could have created spendable XRP beyond the protocols intended total supply. RippleXs October 9 disclosure describes a critical arithmetic bug that had remained in the payment engine since 2015. The project states it found no evidence of exploitation on any public network. Developers released xrpld 3.4.1 on September 25; the issue is now patched, not an active confirmed minting event.  The widely repeated 18 trillion XRP example comes from security researcher Cayden Liaos proof-of-concept estimate. It illustrates possible severity; it is not the amount created on Mainnet and not a financial loss.How one payment could overpay hundreds of offers  XRPL payments can consume multiple offers in the native order book. The vulnerable code added the XRP amounts owed across offers using unchecked 64-bit integer arithmetic. If a maliciously constructed group of offers caused the sum to exceed the integers limit, the total could wrap around to a small number. The engine credited each seller for the full sale while charging the buyer the wrapped total.  This was not an everyday overflow condition. The attack required hundreds of attacker-controlled accounts offering tiny amounts of another token in exchange for extraordinarily

20 hours agoIndustry Research
1
...
46
...
1000